Occupational Qualification · C85
Discretionary Grant · UpcomingCybersecurity Analyst
- NQF Level
- NQF Level 5
- Credits
- 173
- Duration
- —
- SAQA ID
- 118986
Official QCTO Registry Profile
Source: SAQA / QCTO registry- SAQA ID
- 118986
- Min Credits
- 173
- Registered
- 2022-04-21
- Re-registration
- 2025-12-31
- Field
- Field 10 - Physical, Mathematical, Computer and Life Sciences
- Sub-field
- Information Technology and Computer Sciences
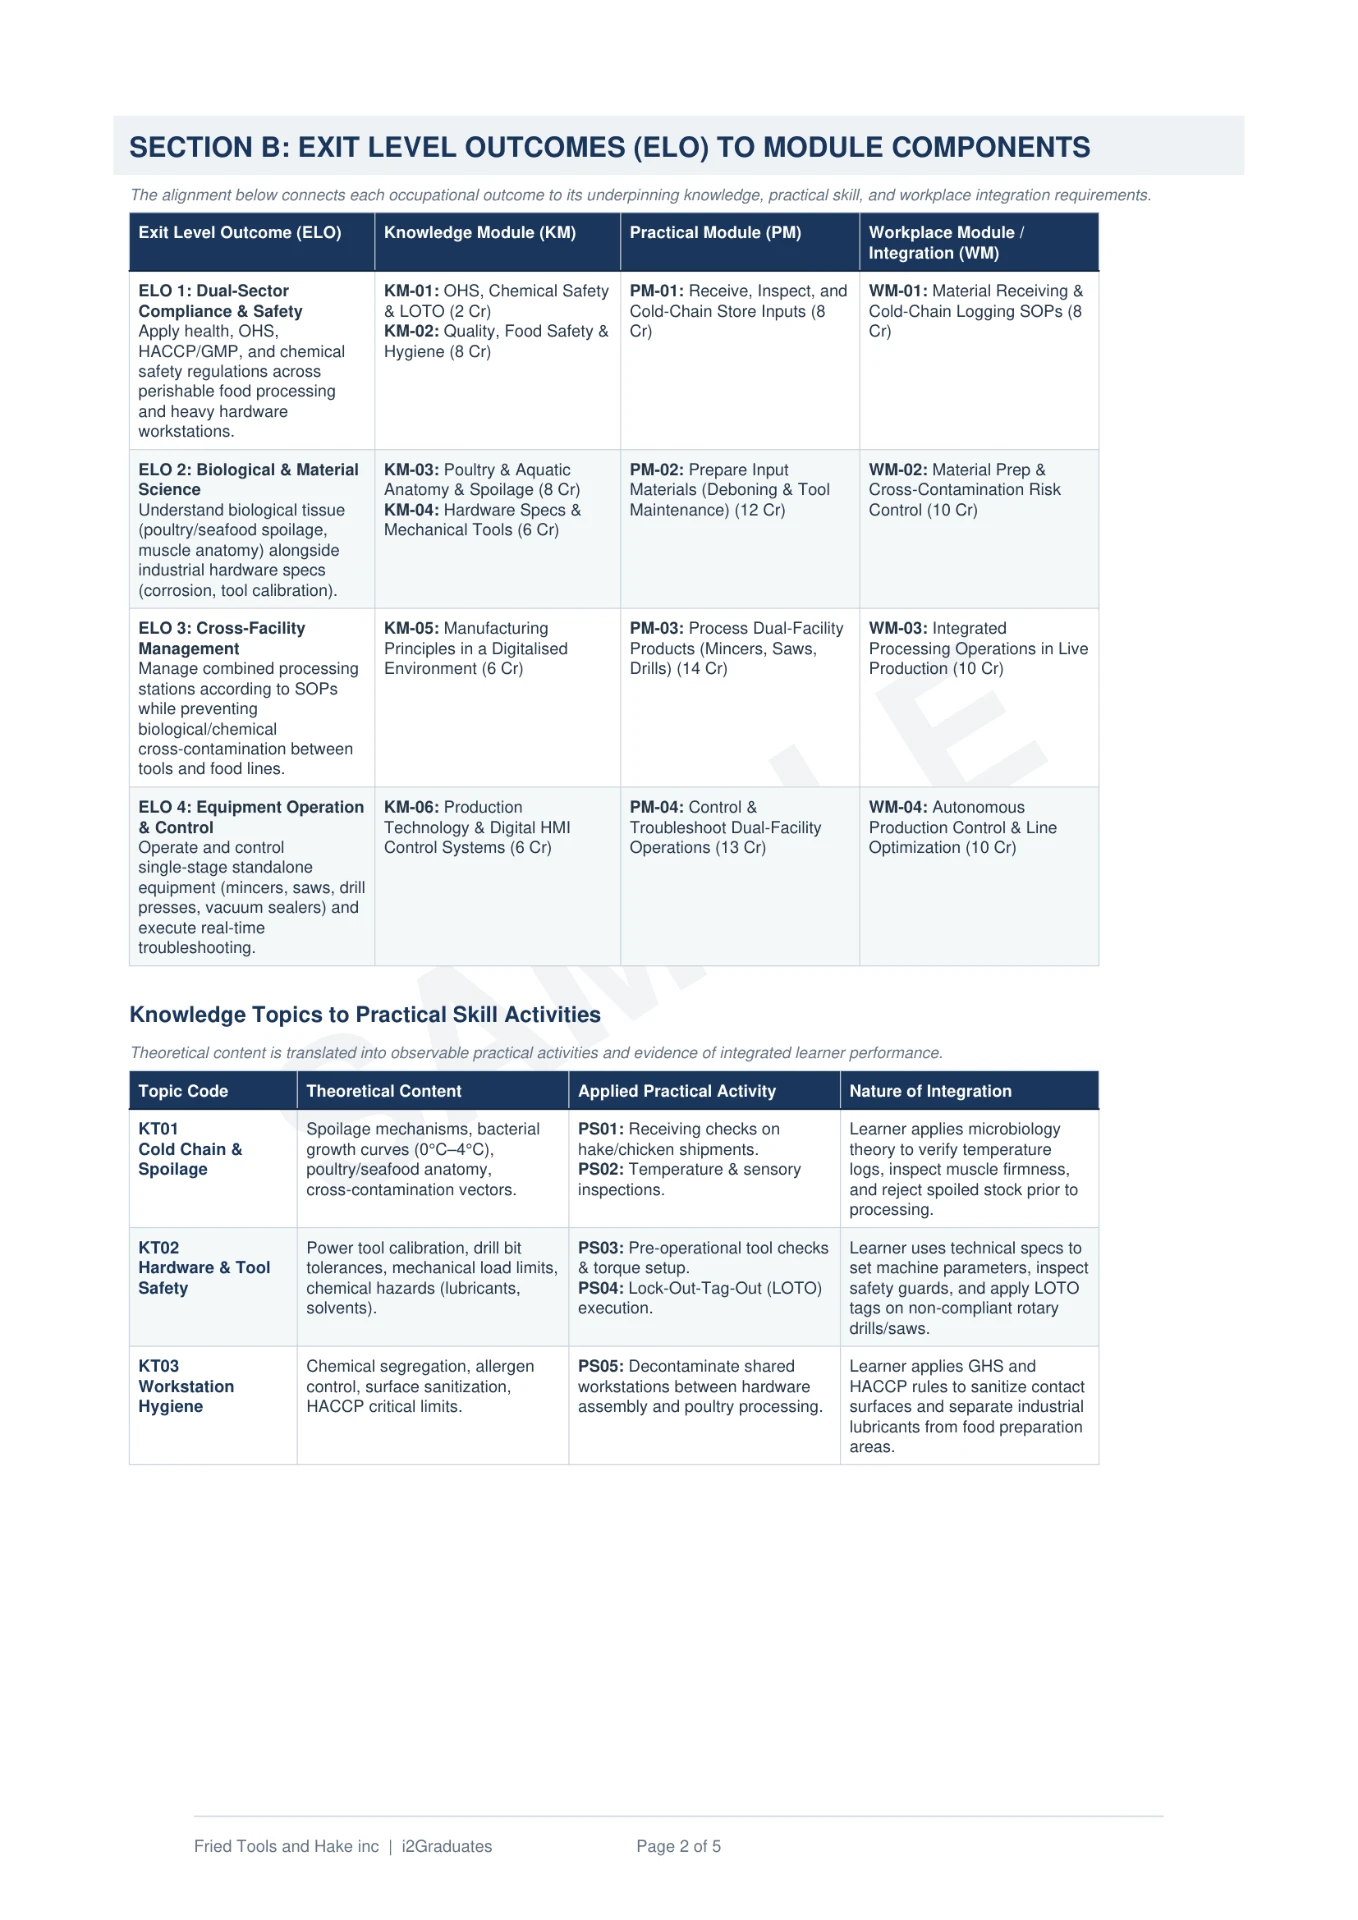
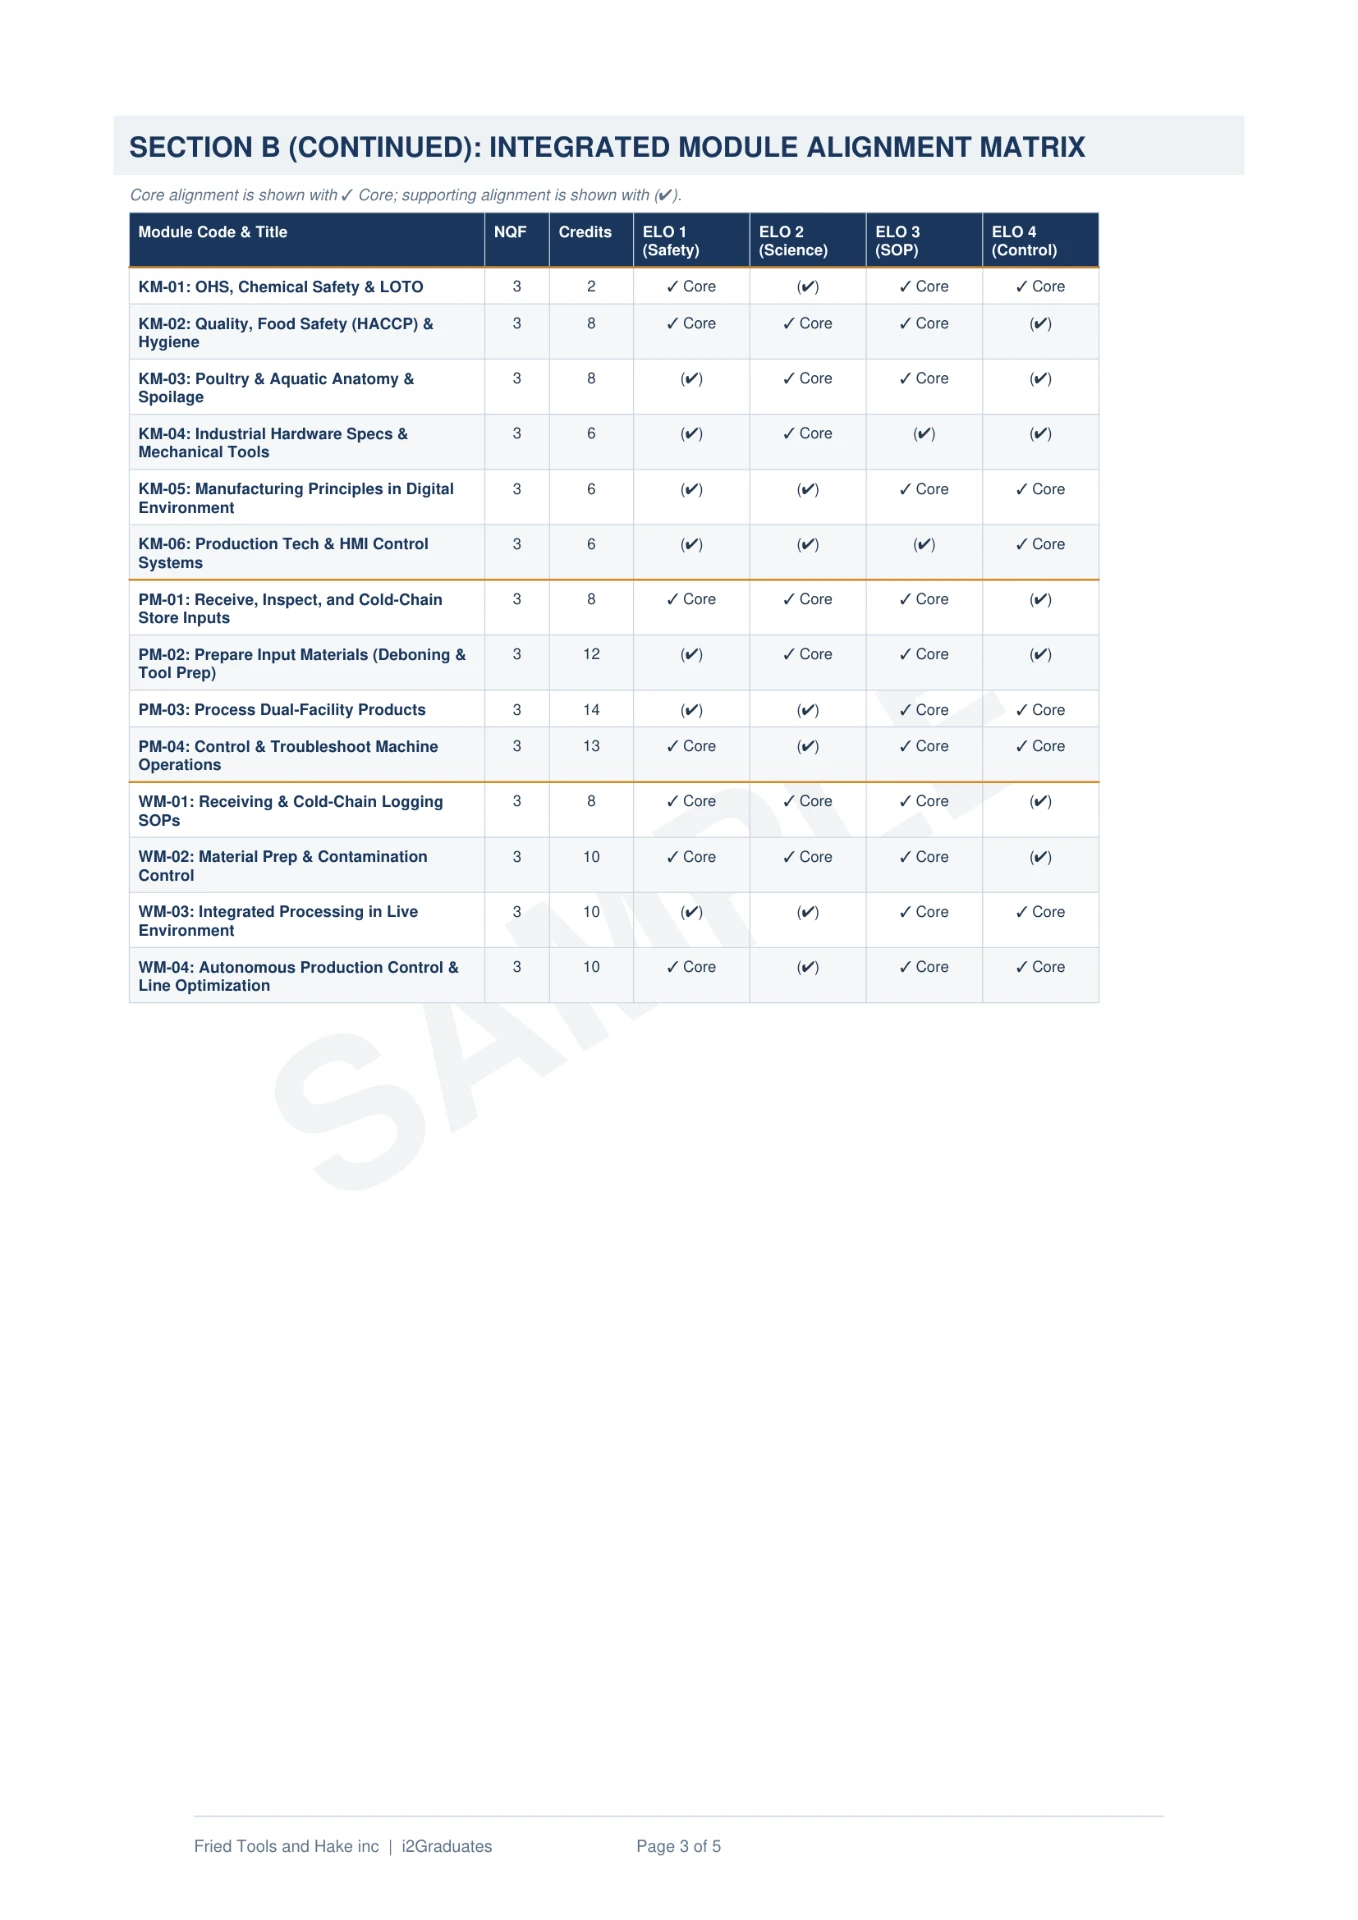
Sample Asset Preview
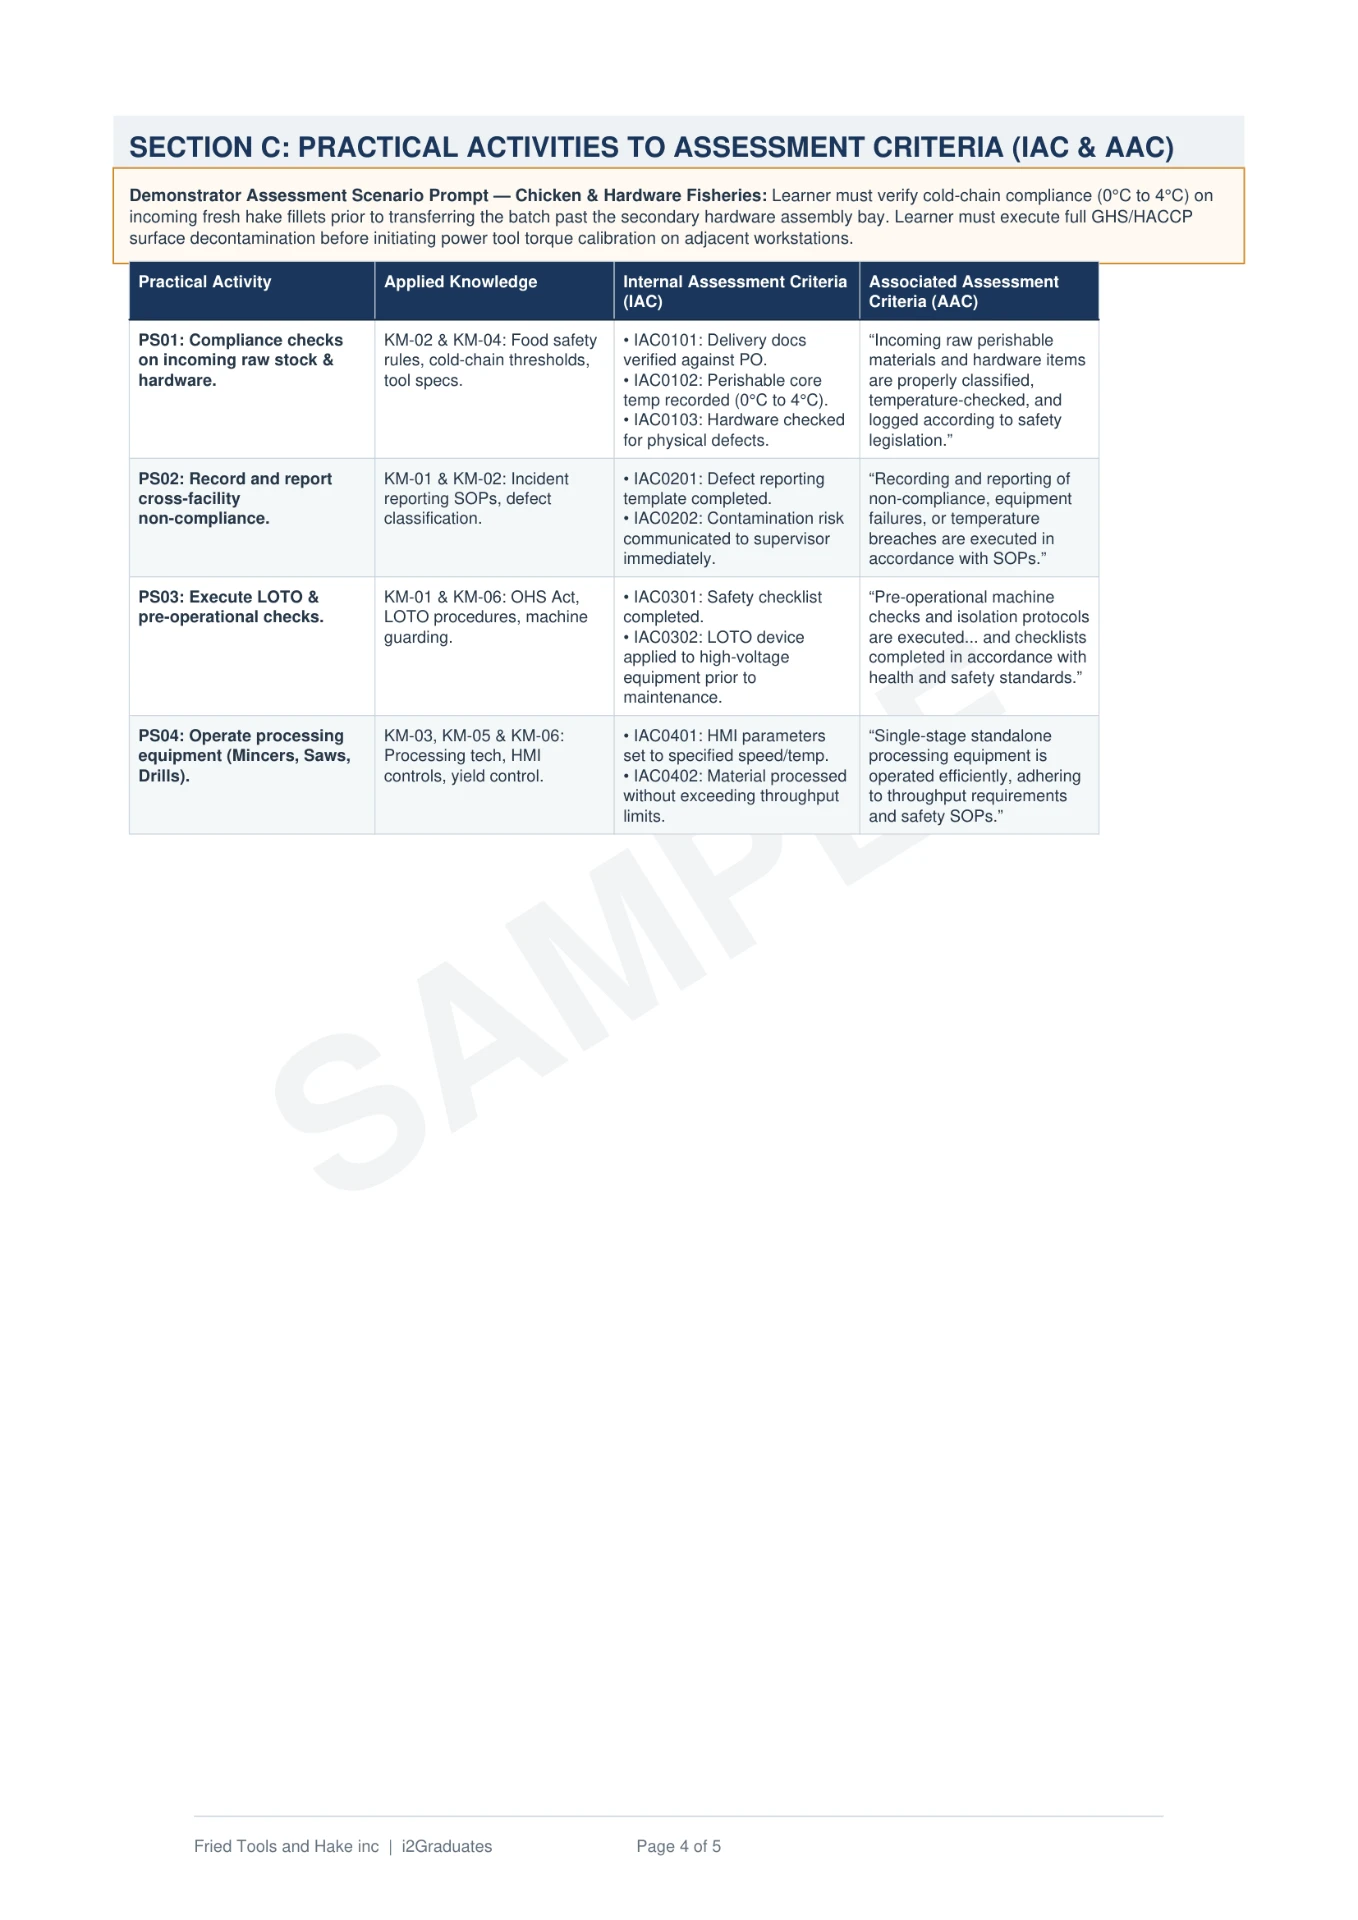
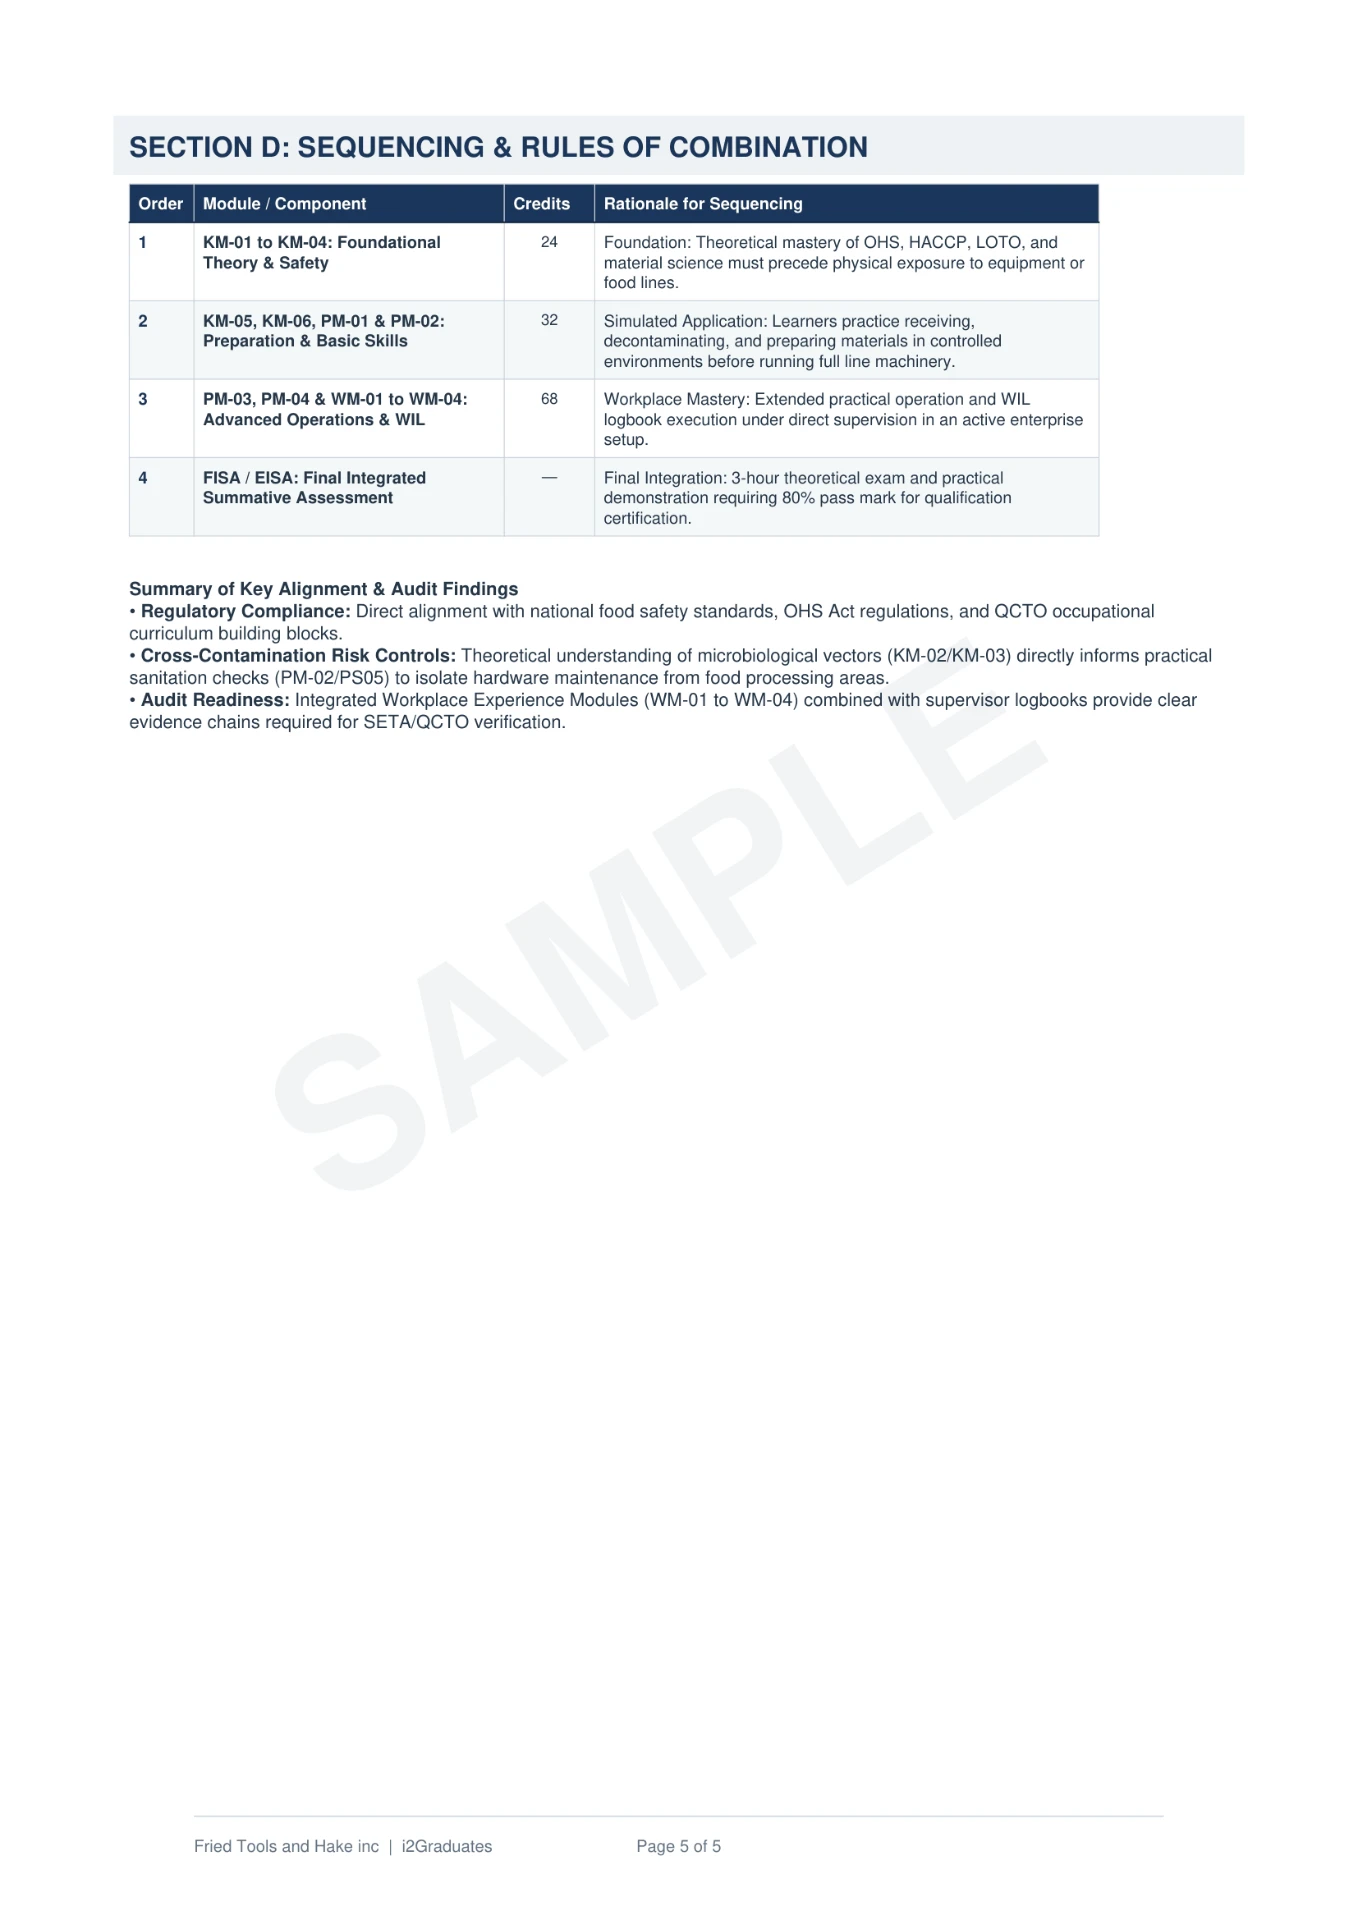
Overview & Scope
Programme Profile
- Target Designation
- Certified Cybersecurity Analyst Practitioner
- Competency Focus
- Master specialised practical applications, safety criteria, and regulatory mandates required of a qualified Cybersecurity Analyst.
- Academic Weight
- Full national recognition at NQF Level 5 yielding 173 credits upon successful PoE verification.
- Work Opportunities
- Deployment across As a qualified cybersecurity analyst, you can find employment opportunities in Information Technology, Media, Communications including private security firms, government facilities, corporate campuses, and event security companies. Your skills will be in demand across both public and private sectors, and you may also choose to work as an independent contractor or start your own business in this field. operations under MICT SETA scope.
- Audit Objective
- Bridges operational skills deficits under the governing MICT SETA quality matrix.
- Value Proposition
- Measurable, legally compliant skills that optimise productivity, satisfy Workplace Skills Plans (WSP), and unlock B-BBEE scorecard weight.
Introduction▾
The Cybersecurity Analyst (NQF Level 5, 173 credits) is a comprehensive Occupational Certificate that blends foundational theory with intensive practical application. Throughout your learning journey, you will develop the competencies required to operate effectively, safely, and ethically within your industry. Employers value this qualification because it signals that you are job-ready from day one.
Purpose▾
The purpose of this qualification is to prepare a learner to operate as a Cybersecurity Analyst. Cybersecurity Analysts apply the practice of protecting assets such as networks, computer systems and information assets from malicious attacks and threats. They assess and mitigate risks and potential intrusions and identify risks and vulnerabilities. They study existing techniques for managing security issues and maintaining the security of information and systems in the working environment, ensuring legal compliance. On completion of this qualification, the learner will be able to demonstrate an understanding of and how to investigate cybersecurity issues and challenges as they affect the legal compliance, communities, society, the ICT sector, and the economy. The learner will understand how cybercrime can affect businesses causing disruption, how to respond effectively to incidences such as vulnerabilities testing and threats and how to analyse their consequences. The learner also evaluates efficient design of efficient security solutions and ensures compliance. A qualified learner will be able to: • Demonstrate knowledge and understanding of cybersecurity concepts. • Investigate how cybersecurity affects legal compliance and solidarity in companies and communities. • Assess risk to assets and evaluate current cybersecurity protection measures. • Implement detection, protection and prevention systems and respond to breaches or incidences.
Entry Requirements▾
Recognition of Prior Learning (RPL): RPL for Access to the Qualification • Learners will gain access to the qualification through RPL for Access as provided for in the QCTO RPL Policy. RPL for access is conducted by accredited education institution, skills development provider or is workplace accredited to offer that specific qualification/part qualification. • Learners who have acquired competencies of the modules of a qualification or part qualification will be credited for modules through RPL. RPL for Access to the External Integrated Summative Assessment Accredited providers and approved workplaces must apply the internal assessment criteria specified in the related curriculum document to establish and confirm prior learning. Accredited providers and workplaces must confirm prior learning by issuing a statement of result. Entry Requirements: The minimum entry requirement for this qualification is: • NQF Level 4 qualification.
SAQA Rationale▾
As Information and Communication Technology (ICT) adoption rates increase so does cybercrime and, in direct relation, the serious need for security and integrity of ICT systems is recognised as being of paramount importance. The urgent need and demand for competent personnel have been increasing over time. There is a global shortage of cybersecurity experts, and this number is diminishing every year. The recently published 2019 (ISC) 2 Cybersecurity Workforce Study pointed to a severe shortage of cybersecurity professionals. The study estimated, for the first time, that there are 2.8 million skilled professionals worldwide currently working in the field and that an additional 4.07 million more are needed to defend organizations. Acquiring this qualification will assist in fulfilling the obvious and serious need for cyber security experts, will have a direct, positive impact on the ICT sector and will consequently benefit the economy as well. The global cybersecurity market size is forecasted to grow to ZAR 3764 billion by 2023. In Africa the cyber security market size grows from ZAR 14 billion in 2015 to ZAR35 Billion by 2020, at a Compound Annual Growth Rate (CAGR) of 20.41% from 2015 to 2020. According to 6Wresearch, South Africa's Cyber Security Market size is projected to register a CAGR of 11.1% during 2020-26. There are no similar qualifications registered on the NQF other than those used as articulation possibilities in the section below and no professional registration or licencing is expected for Cybersecurity Analysts to seek employment in the sector. Through the growth of Cyber Security Analysts that have completed this qualification, it is expected that there will be a measurable reduction in Cyber Crime-related disruption in business continuity, a reduction in losses incurred and an increase in the number of perpetrators brought to justice. It will also provide a remedy to the severe shortage of cybersecurity professionals in Africa. Cybersecurity Analysts can be employed as Cybersecurity Specialists, Information Security Specialists, Security Analysts, Cyber Monitoring Analysts, Security Consultants or Network Security Analysts. Typical learners include school leavers, graduates from TVET colleges and those currently in employment without formal recognition of competencies. This qualification will support the recommendations of the Presidential Commission on the 4th Industrial Revolution. This recommendations forefront human capital and the future of work and refers to growing skills instability. It states that work will change, and that robotic process automation (RPA) will play a more pivotal role in the execution of tasks. The 4th Industrial Revolution (4IR) is a fusion of advances in artificial intelligence (AI), robotics, process automation, the Internet of Things (IoT), genetic engineering, quantum computing, cyber security, cloud computing and data science.
Learning Assumed to be in Place & RPL▾
Recognition of Prior Learning (RPL): RPL for Access to the Qualification • Learners will gain access to the qualification through RPL for Access as provided for in the QCTO RPL Policy. RPL for access is conducted by accredited education institution, skills development provider or is workplace accredited to offer that specific qualification/part qualification. • Learners who have acquired competencies of the modules of a qualification or part qualification will be credited for modules through RPL. RPL for Access to the External Integrated Summative Assessment Accredited providers and approved workplaces must apply the internal assessment criteria specified in the related curriculum document to establish and confirm prior learning. Accredited providers and workplaces must confirm prior learning by issuing a statement of result. Entry Requirements: The minimum entry requirement for this qualification is: • NQF Level 4 qualification.
Exit Level Outcomes▾
- Analyse, identify, and solve potential and actual security risks, vulnerabilities and inefficiencies to safeguard information system assets from malicious cybersecurity attacks.
- Protect organisation's digital assets from both internal and external threats by maintaining cybersecurity attack mitigation and incident response capability.
- Execute ethical cybersecurity monitoring in line with cybersecurity policies to provide defence to a level of confidentiality, integrity, and availability equal with the threat to assets and their value to the company.
- Execute response procedures to mitigate cyber-attacks and secure information assets, intellectual property, and computer systems.
- Execute recovery protocols and procedures as per recovery plan to restore data and/or assets affected by cybersecurity incidents.
Learning Material Included
- Learner Guide (Theory and Knowledge Modules)
- Facilitator Guide
- Workplace Logbook
- Formative and Summative Assessment
- Assessor Guide & Marking Memorandum
- SETA / QCTO Alignment Matrix
- Administrative & Onboarding Pack
- Implementation Plan
Moderator-Ready Curriculum Breakdown
19 modules · 169 creditsTheory, regulatory and safety knowledge. Each row carries the registered module code, NQF level and credit weight used for formative assessment rubric mapping.
- 252901-001-00-KM-018 cr
Introduction to Cybersecurity
NQF Level 4
- 252901-001-00-KM-0212 cr
Fundamentals of Network Security and Defence
NQF Level 5
- 252901-001-00-KM-0312 cr
Cybersecurity and Cyber Threats and Attacks
NQF Level 5
- 252901-001-00-KM-051 cr
Fundamentals of Design Thinking and Innovation
NQF Level 4
- 252901-001-00-KM-063 cr
Logical Thinking and Basic Calculations
NQF Level 4
- 252901-001-00-KM-076 cr
Computers, Devices and Computing Systems
NQF Level 4
- 252901-001-00-KM-083 cr
Data and Database Vulnerabilities
NQF Level 4
- 252901-001-00-KM-094 cr
Introduction to 4IR and Future Skills
NQF Level 4
Qualification 118986 · Curriculum Architecture
Occupational Certificate: Cybersecurity Analyst · NQF Level 5 (173 Credits)
Three Curriculum Pillars
Knowledge Modules
Classroom & E-Learning
- Facilitated lectures & self-study
- Written question banks
- Formative comprehension checks
Practical Skill Modules
Simulated Line Tasks
- Simulated line tasks
- Observation rubrics
- Structured task sheets
Work Experience Modules
On-the-Job Production
- On-the-job rotation
- Mentor logbooks
- Workplace sign-offs
Evidence & Audit Pipeline
Learner Portfolio of Evidence (PoE)Owner · Candidate▾
Admin & Registration
ID, learner contract, induction pack, POPIA consent.
Knowledge Evidence
Written assessments & question banks — KM-01 to KM-07.
Practical Evidence
Task sheets, observation rubrics, assessor photos.
Workplace Evidence
Logbooks, mentor sign-offs, supervisor letters.
Assessor Master FileOwner · Registered Assessor▾
Assessment Reports
Judgements, learner feedback, remediation agreements, appeals log.
Internal Moderation & Quality FileOwner · Moderator / SDP▾
Moderation Evidence
10% sampling matrix, HACCP/LOTO compliance sheets, SDP sign-off.
Final Accreditation Gateway
Issued by the accredited Skills Development Provider once internal moderation is signed off.
Provider submits declaration + PoE to the Assessment Quality Partner (AQP).
QCTO awards the SAQA-registered certificate on successful EISA outcome.
Audit & Compliance
Evidence & Audit Pipeline
From portfolio assembly to external sign-off — the exact route your evidence travels.
- Step 1
PoE Assembly
Learner evidence, formative records and logbook entries filed against the alignment matrix.
- Step 2
Internal Assessment
Registered assessor judges each KM/PM/WM outcome using the supplied instruments.
- Step 3
Internal Moderation
Sampling and verification of assessor decisions, with remediation loop before submission.
- Step 4
External Moderation
SETA/QCTO desktop audit and certification upload against registered credits.
Broken Standard vs i2Graduates Standard
The measurable delta between improvised material and an audit-ready suite.
Broken Standard
i2Graduates Standard
Curriculum Mapping
Photocopied guides with mismatched outcomes
8 KM + 8 PM + 3 WM modules mapped to NQF Level 5
Assessment Bank
Missing formative and summative assessments
Pre-validated assessment bank per module
Alignment Evidence
No alignment matrix — audit fails
MICT SETA alignment matrix included
Facilitation
Facilitators improvise Cybersecurity Analyst delivery
Facilitator scripts + learner activities per credit
Portfolio of Evidence
PoE gaps flagged in moderation
PoE templates that survive external moderation
Pricing & Delivery Tiers
Base licence from R63 650
Digital Master Suite
Editable master files, licensed to your SDP
- Learner Guide, Facilitator Guide & Assessment Suite
- Workplace logbook + alignment matrix (editable)
- Instant digital delivery under institutional licence
- Free minor corrections for 12 months
Turnkey Print & Bound Package
Printed, bound and couriered per learner
- Everything in the Digital Master Suite
- Full-colour print, wire-bound learner packs
- Per-learner PoE folders and dividers
- Nationwide courier with tracked delivery
Full Enterprise Accreditation Bundle
Assets plus accreditation support end-to-end
- Everything in the Print & Bound Package
- Bespoke QMS build mapped to your scope
- Moderation dry-run + written remediation report
- Brand & metadata integration across the suite
Complementary Services
Optional add-ons that harden your accreditation scope before an external audit.
Bespoke QMS Build
We author your Quality Management System — policies, procedures, records, matrices — mapped to your accreditation scope. From R18,500.
Request QuoteModeration Consultation
External moderation dry-run on your PoE + delivery pack. Written report with fixes before your real audit. From R4,900.
Book Moderation SessionThe i2Graduates Quality Guarantee
Every page of this bundle is checked for sequence and structural accuracy — no missing pages, no shortcuts. You get pre-validated assessment instruments ready to survive rigorous compliance moderation, wrapped in a curriculum your facilitators will enjoy teaching.