Occupational Qualification · C21
Discretionary Grant · UpcomingChief Information Officer: Cybersecurity
- NQF Level
- NQF Level 7
- Credits
- 120
- Duration
- —
- SAQA ID
- 121968
Official QCTO Registry Profile
Source: SAQA / QCTO registry- SAQA ID
- 121968
- Min Credits
- 120
- Registered
- 2024-01-30
- Re-registration
- 2029-01-30
- Field
- Field 10 - Physical, Mathematical, Computer and Life Sciences
- Sub-field
- Information Technology and Computer Sciences
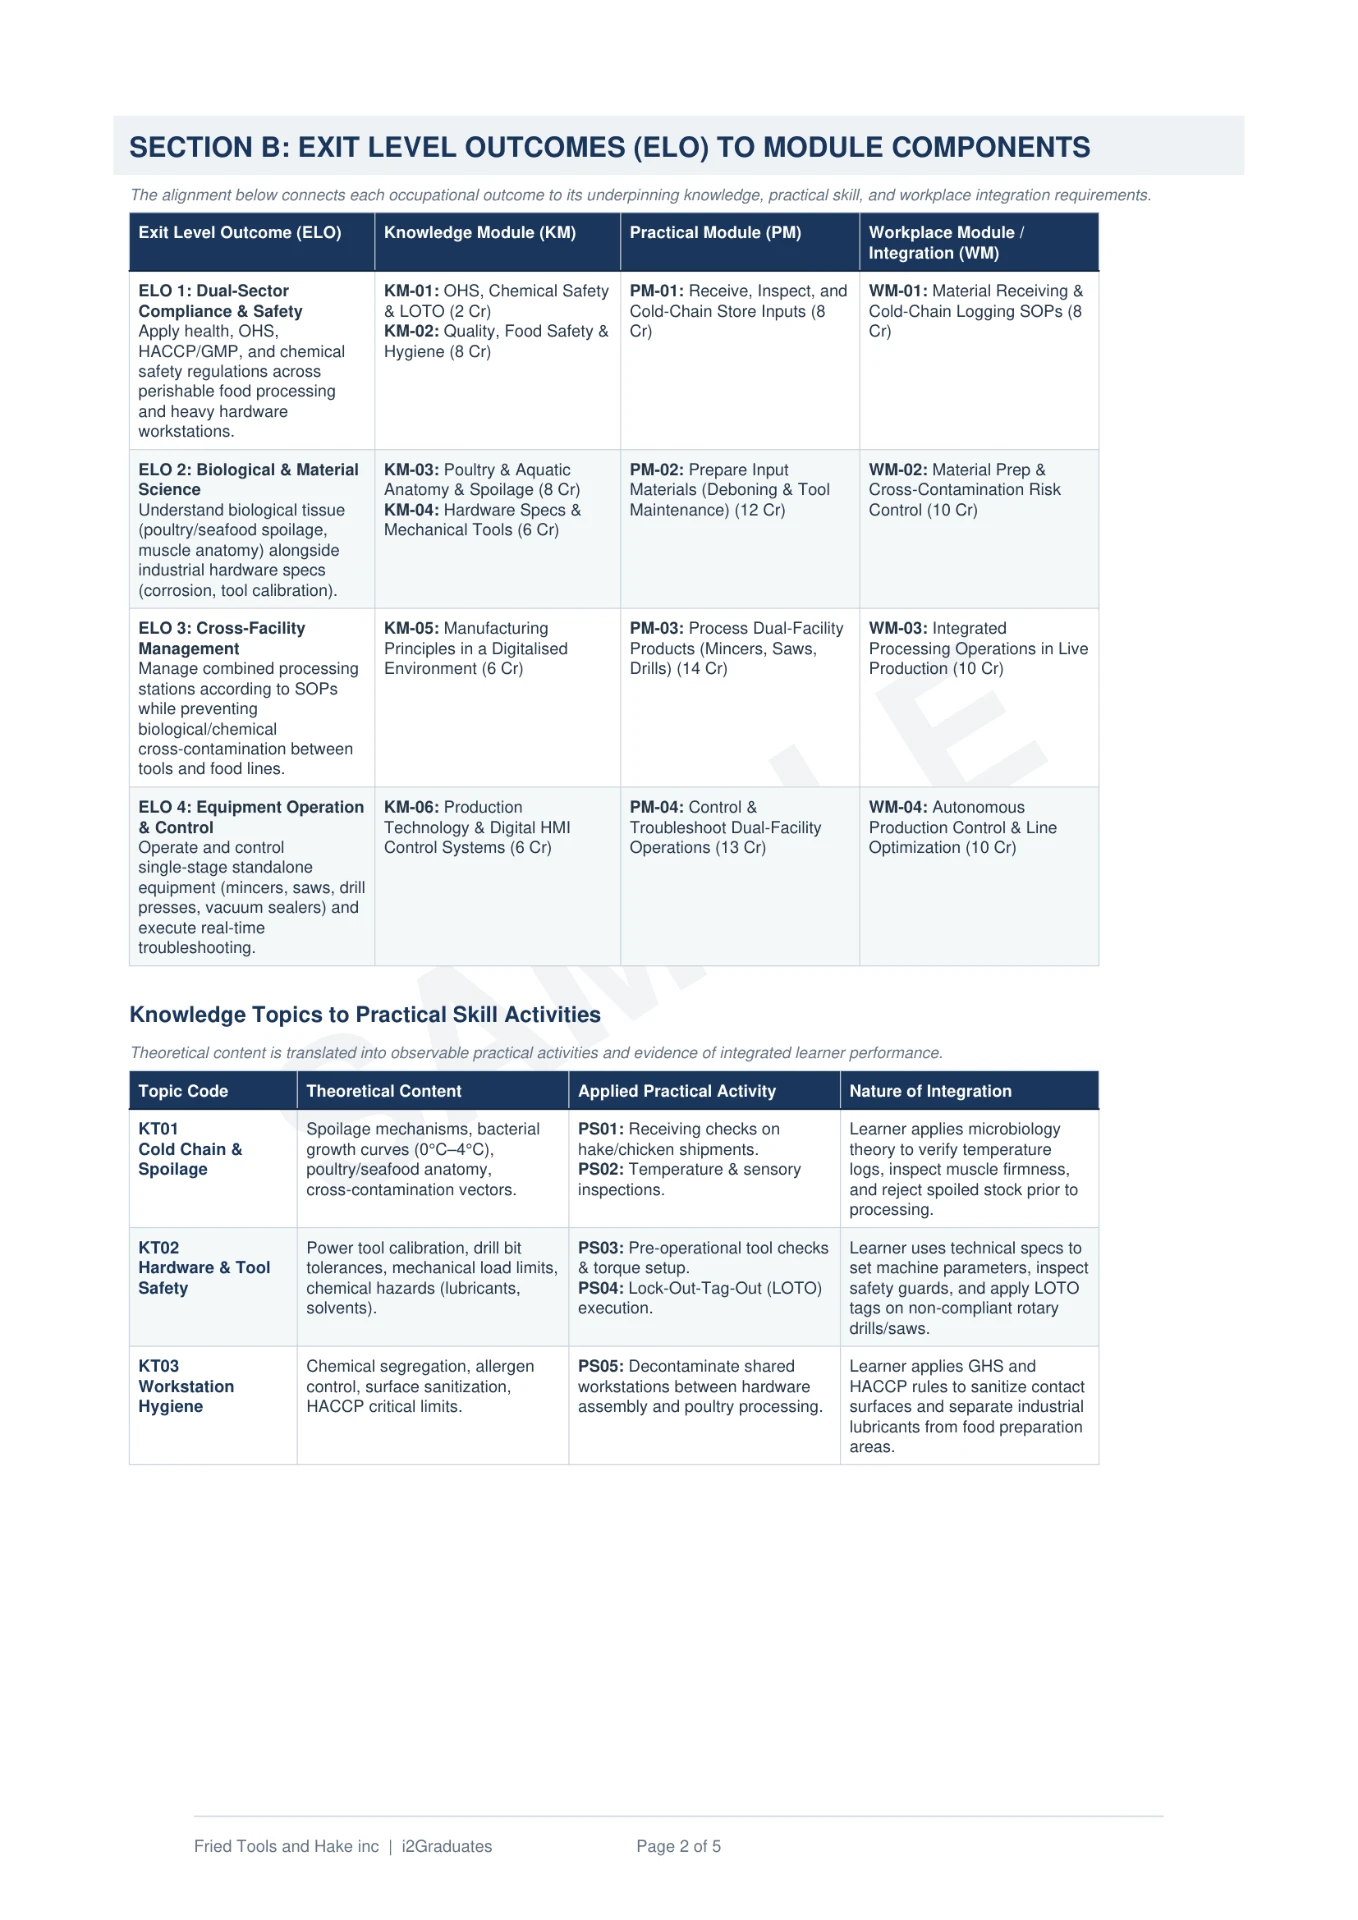
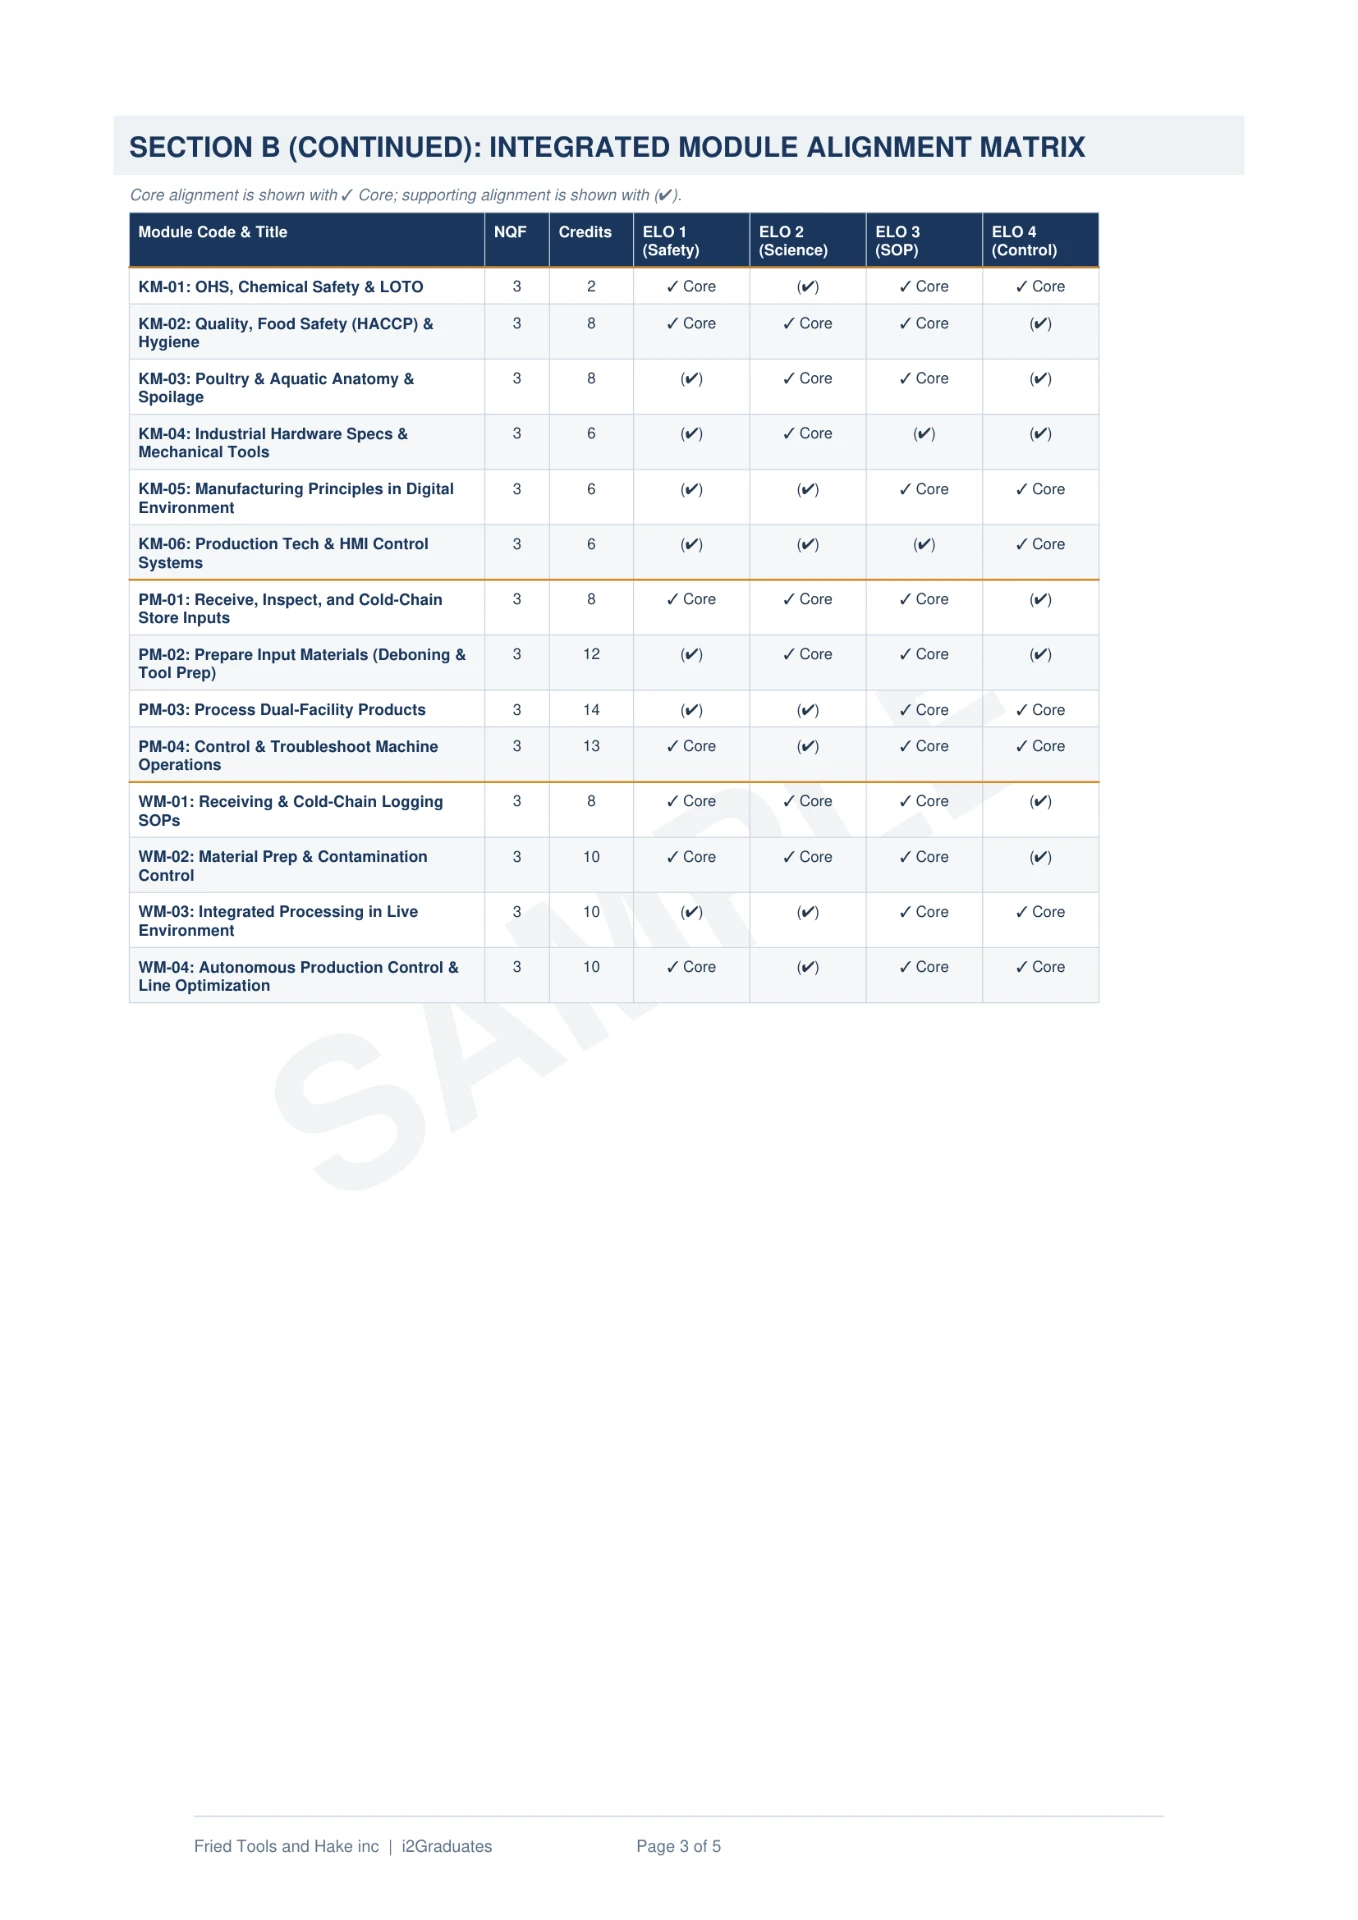
Sample Asset Preview
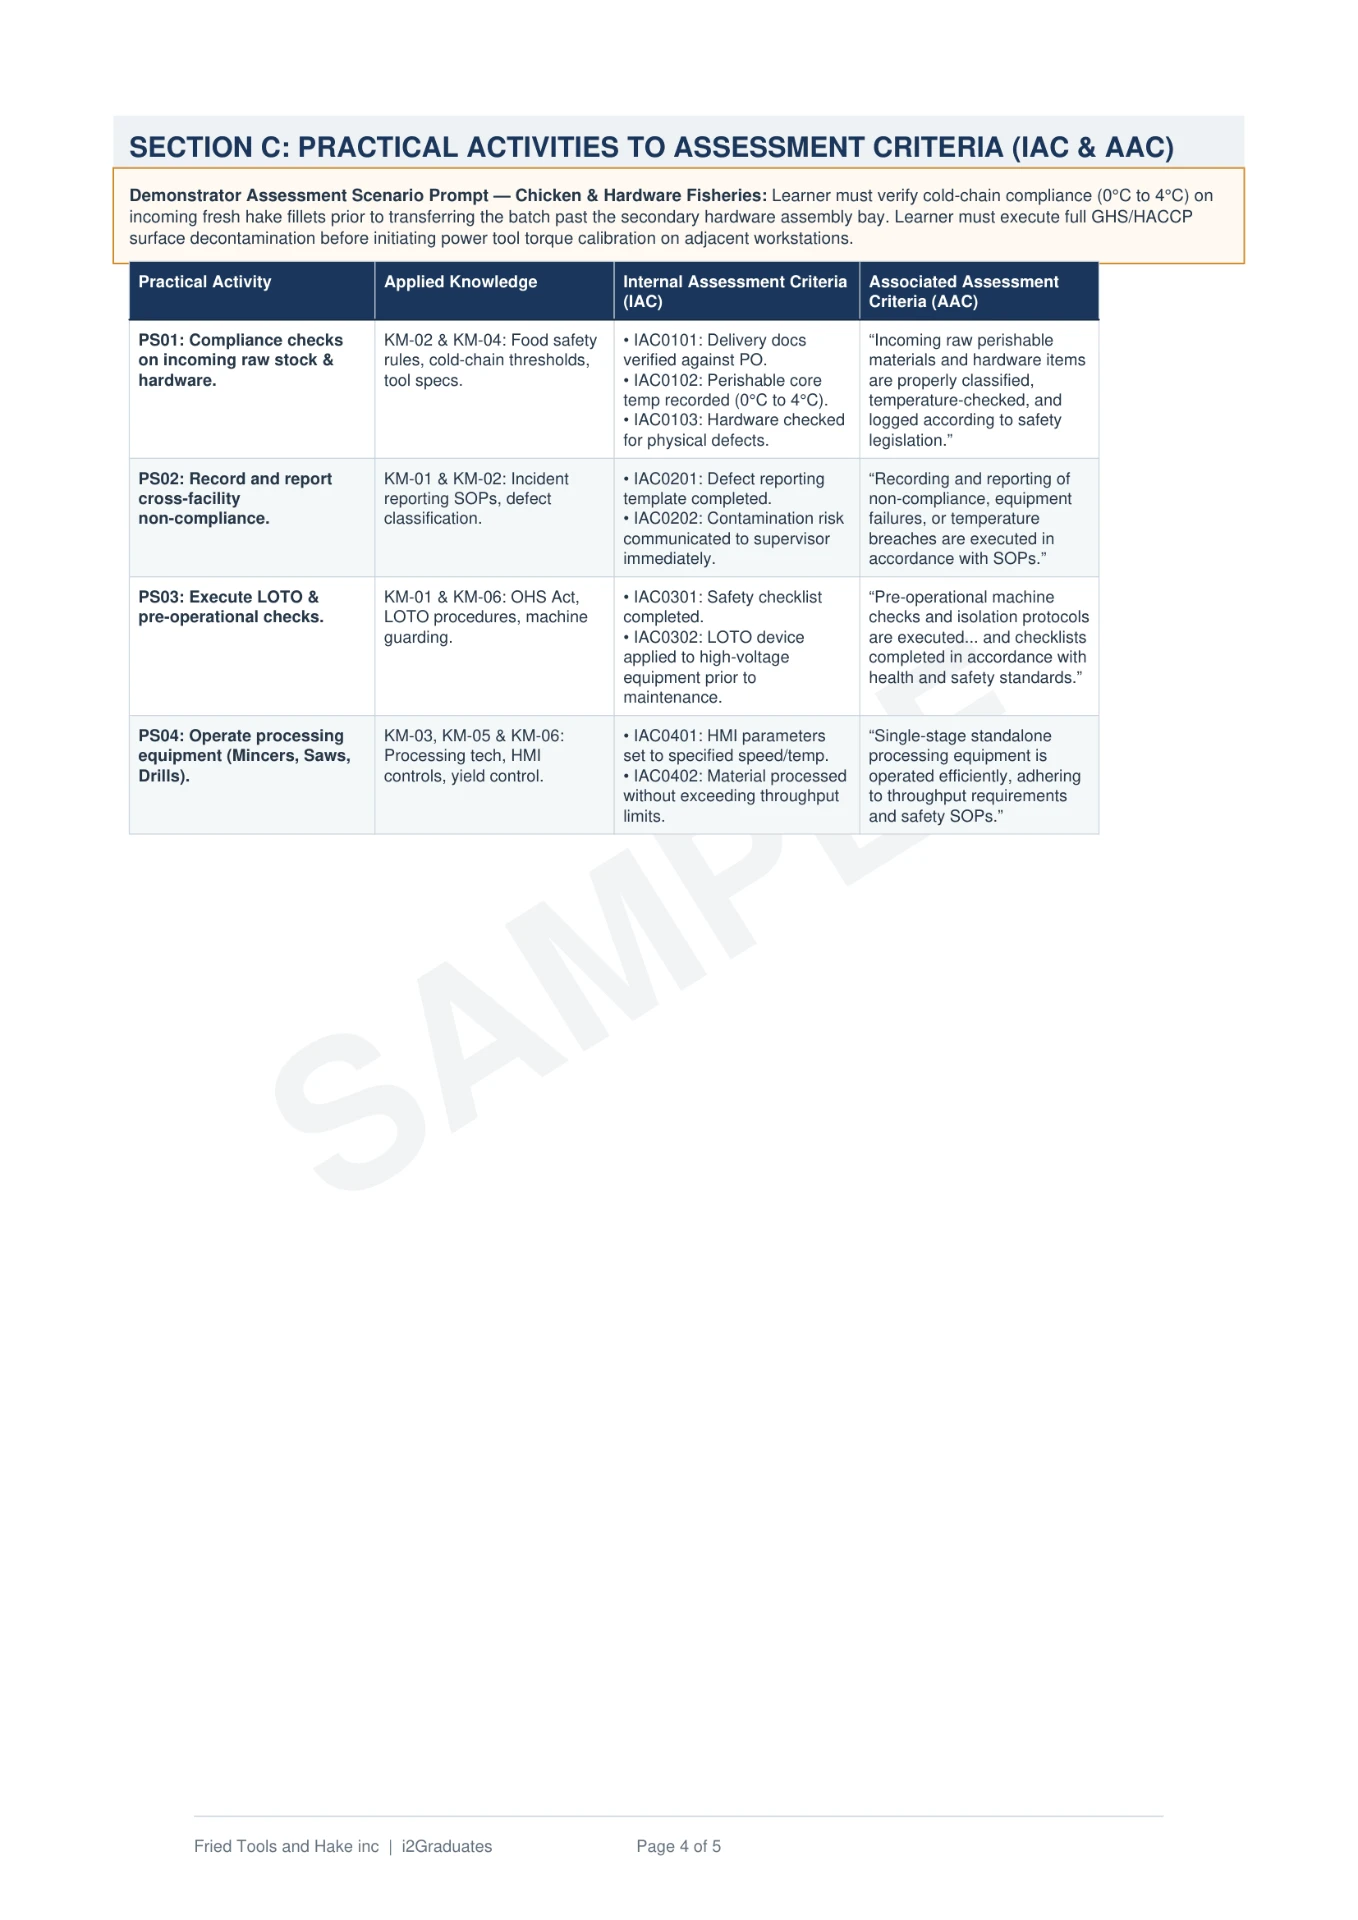
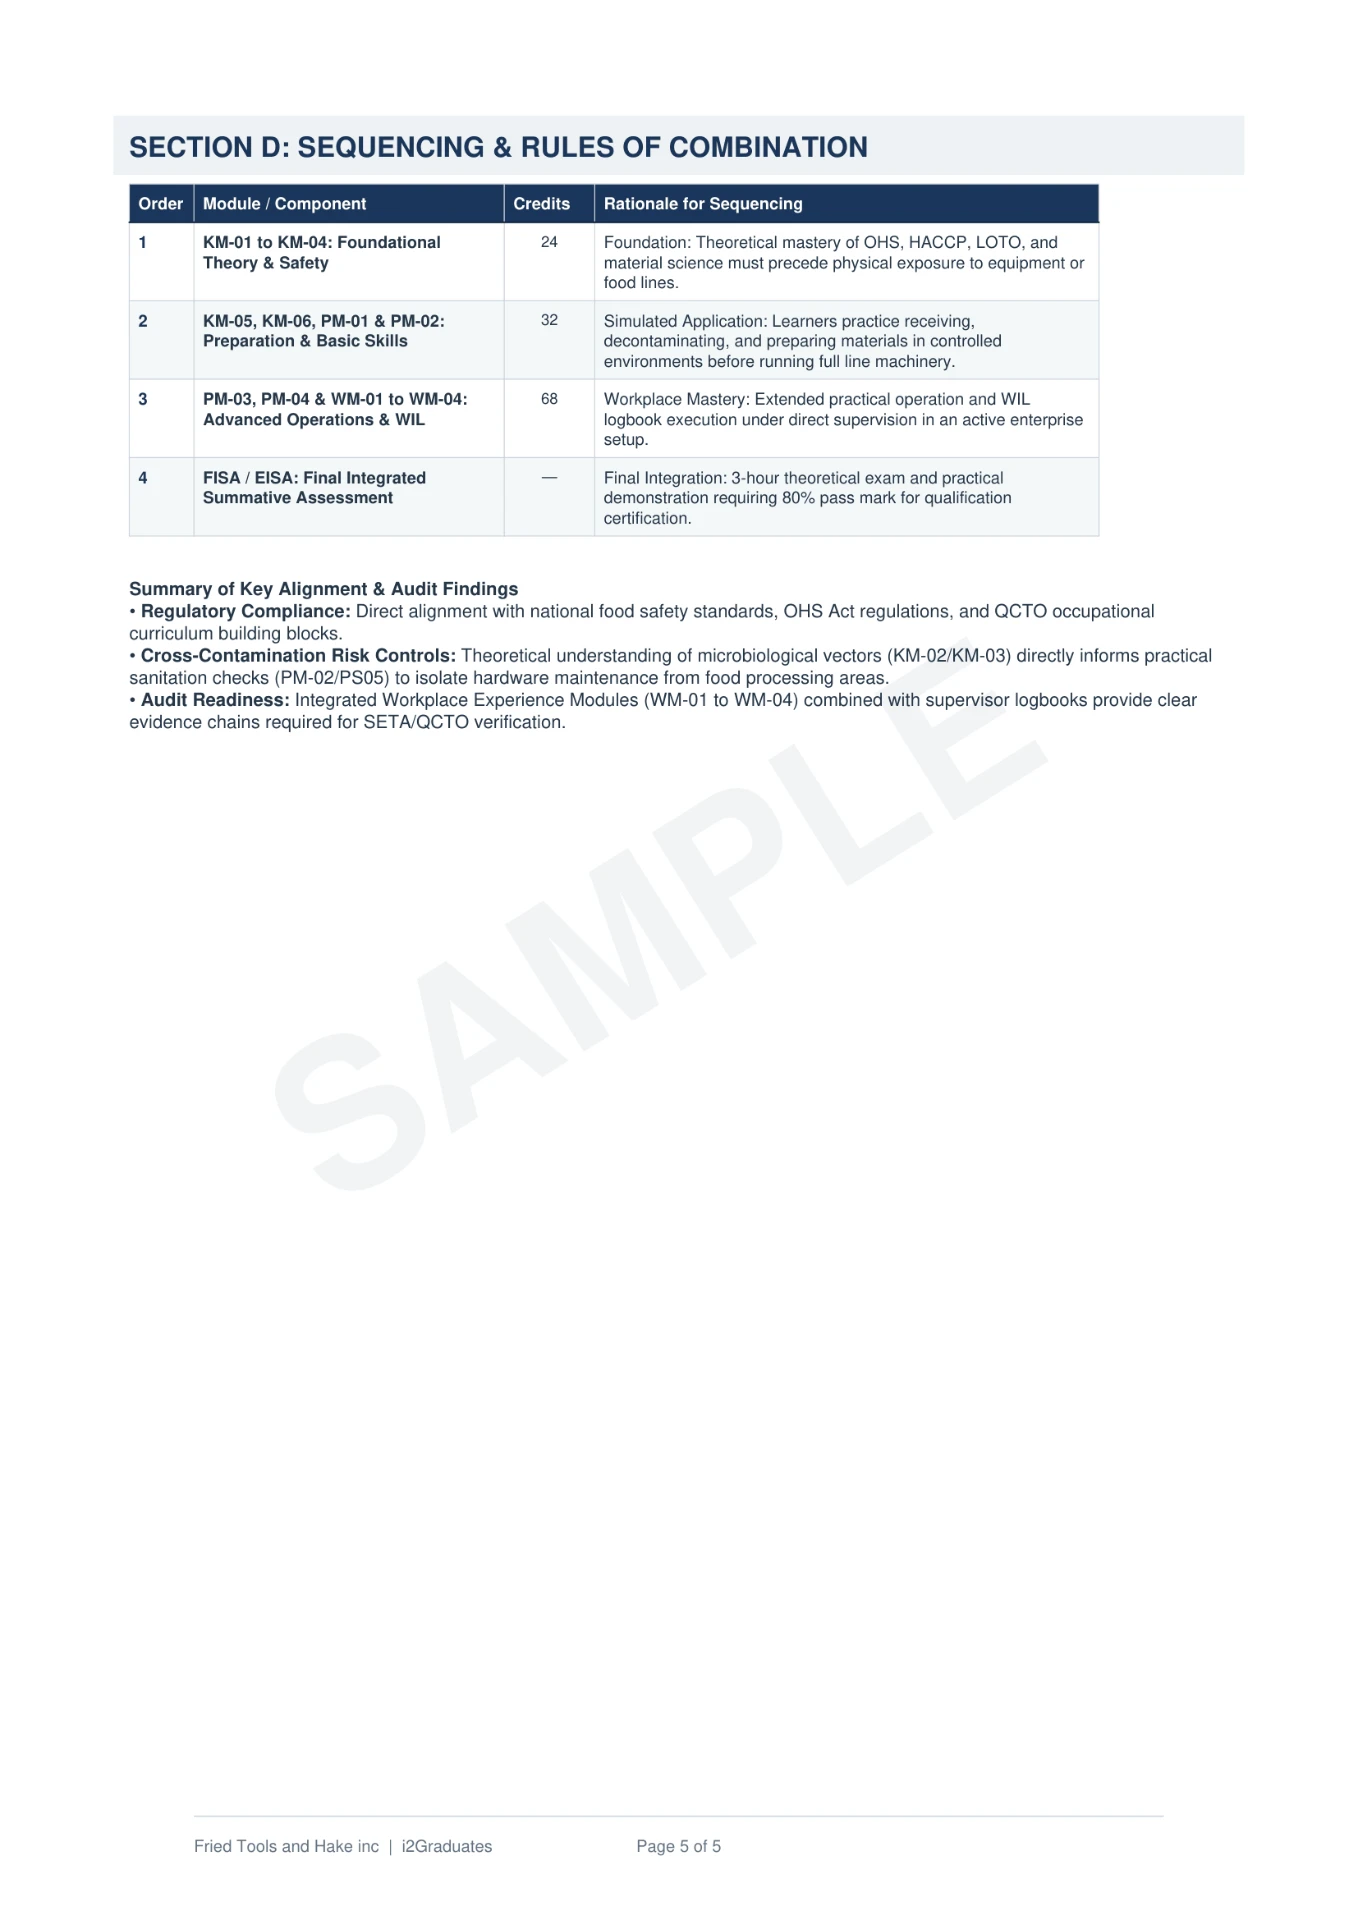
Overview & Scope
Programme Profile
- Target Designation
- Certified Chief Information Officer: Cybersecurity Practitioner
- Competency Focus
- Master specialised practical applications, safety criteria, and regulatory mandates required of a qualified Chief Information Officer: Cybersecurity.
- Academic Weight
- Full national recognition at NQF Level 7 yielding 120 credits upon successful PoE verification.
- Work Opportunities
- Deployment across As a qualified chief information officer: cybersecurity, you can find employment opportunities in Banking, Financial Services including private security firms, government facilities, corporate campuses, and event security companies. Your skills will be in demand across both public and private sectors, and you may also choose to work as an independent contractor or start your own business in this field. operations under BANKSETA scope.
- Audit Objective
- Bridges operational skills deficits under the governing BANKSETA quality matrix.
- Value Proposition
- Measurable, legally compliant skills that optimise productivity, satisfy Workplace Skills Plans (WSP), and unlock B-BBEE scorecard weight.
Introduction▾
The Chief Information Officer: Cybersecurity (NQF Level 7, 120 credits) is a comprehensive Advanced Occupational Diploma that blends foundational theory with intensive practical application. Throughout your learning journey, you will develop the competencies required to operate effectively, safely, and ethically within your industry. Employers value this qualification because it signals that you are job-ready from day one.
Purpose▾
The purpose of this qualification is to prepare a learner to operate as a Chief Information Officer: Cybersecurity. A Chief Information Officer: Cybersecurity ensures the effective and holistic management of the risks, threats and resiliency of cybersecurity within an organisation. This could include information security, fraud and physical security. They are accountable to build cybersecurity vigilance and resiliency across the operations, leveraging best in class capabilities and processes relating to threat analysis, threat intelligence, protection tools and subject matter expertise. The Chief Information Officer: Cybersecurity is accountable for protecting the organisations, its customers and its employees, as well as society at large, from the negative effects of cyber-crime and fraud. A competent learner will demonstrate among others the following key attributes: complex thinking, deft communication, diplomacy, executive leadership, strategic orientation, critical thinking, emotional intelligence, analytical skills. A qualified learner will be able to: • Oversee the cybersecurity function; and • Lead the provision of secure Information Technology systems.
Entry Requirements▾
Recognition of Prior Learning: • Learners will gain access to the qualification through RPL for Access as provided for in the QCTO RPL Policy. RPL for access is conducted by accredited education institution, skills development provider or workplace accredited to offer that specific qualification/part qualification. • Learners who have acquired competencies of the modules of a qualification or part qualification will be credited for modules through RPL. RPL for access to the external integrated summative assessment: Accredited providers and approved workplaces must apply the internal assessment criteria specified in the related curriculum document to establish and confirm prior learning. Accredited providers and workplaces must confirm prior learning by issuing a statement of result. Entry Requirements: • NQF Level 6 qualification in Information Technology, Computer Science or Cybersecurity.
SAQA Rationale▾
There is a shortage of cybersecurity professionals, particularly for positions in governments, which create high levels of risk. Current Information Technology professionals may not be fully trained in information security tactics, strategy and leadership. They help develop new ways to combat cyber threats, and are the main line of defence against spamming, phishing, malware, viruses, and other information security threats. As cyber-attacks have increased, so has the demand for trained professionals to prevent and counter such attacks. Organisations rely more heavily on technology to help manage their daily lives, as such the threat of cyber-crime continues to escalate. Economies lose billions of dollars and, governments are threatened by the risks posed by nefarious attacks on the key digital systems. In recent years, large-scale cyber-attacks have affected major companies. Data breaches compromise personal information, bank records, credit card numbers and other private information, including usernames, passwords, emails, phone numbers and addresses. Information Technology professionals shall hone their skills through this cybersecurity qualification and benefit the organisations. It shall enable learners to devise strategies and methods to prevent and counter cyber-attacks on both public and private organisations, thus saving millions of revenues in potential loss of trust from clients and service provision. Typical learners for the qualification are those who are employed as Cybersecurity practitioners wishing to advance to managerial and leadership roles in cybersecurity. This qualification will enable cybersecurity officials to progress to specialist roles, middle and senior management levels. The holders of qualification do not require professional registration to practice. The qualification also provides a unique tool to facilitate appropriate recognition of learning gained over time. It will promote high standards of safety within the digital economy, as part of the national development plan. This qualification supports the economic development needs of society. The qualification was developed in collaboration with the Information and Communication Technology Sector, central and commercial banking sectors.
Learning Assumed to be in Place & RPL▾
Recognition of Prior Learning: • Learners will gain access to the qualification through RPL for Access as provided for in the QCTO RPL Policy. RPL for access is conducted by accredited education institution, skills development provider or workplace accredited to offer that specific qualification/part qualification. • Learners who have acquired competencies of the modules of a qualification or part qualification will be credited for modules through RPL. RPL for access to the external integrated summative assessment: Accredited providers and approved workplaces must apply the internal assessment criteria specified in the related curriculum document to establish and confirm prior learning. Accredited providers and workplaces must confirm prior learning by issuing a statement of result. Entry Requirements: • NQF Level 6 qualification in Information Technology, Computer Science or Cybersecurity.
Exit Level Outcomes▾
- Oversee the cybersecurity function within the ethical, legal and professional context.
- Lead the provision of secure Information Technology systems using a range of enquiry methods.
Learning Material Included
- Learner Guide (Theory and Knowledge Modules)
- Facilitator Guide
- Workplace Logbook
- Formative and Summative Assessment
- Assessor Guide & Marking Memorandum
- SETA / QCTO Alignment Matrix
- Administrative & Onboarding Pack
- Implementation Plan
Moderator-Ready Curriculum Breakdown
2 modules · 40 creditsTheory, regulatory and safety knowledge. Each row carries the registered module code, NQF level and credit weight used for formative assessment rubric mapping.
- 133101-001-00-KM-0120 cr
Management, Leadership and Governance Principles within a Cybersecurity Context
NQF Level 7
- 133101-001-00-KM-0220 cr
Concepts and Principles Underpinning the Provisioning of Secure ICT within an Enterprise
NQF Level 7
Qualification 121968 · Curriculum Architecture
Advanced Occupational Diploma: Chief Information Officer: Cybersecurity · NQF Level 7 (120 Credits)
Three Curriculum Pillars
Knowledge Modules
Classroom & E-Learning
- Facilitated lectures & self-study
- Written question banks
- Formative comprehension checks
Practical Skill Modules
Simulated Line Tasks
- Simulated line tasks
- Observation rubrics
- Structured task sheets
Work Experience Modules
On-the-Job Production
- On-the-job rotation
- Mentor logbooks
- Workplace sign-offs
Evidence & Audit Pipeline
Learner Portfolio of Evidence (PoE)Owner · Candidate▾
Admin & Registration
ID, learner contract, induction pack, POPIA consent.
Knowledge Evidence
Written assessments & question banks — KM-01 to KM-07.
Practical Evidence
Task sheets, observation rubrics, assessor photos.
Workplace Evidence
Logbooks, mentor sign-offs, supervisor letters.
Assessor Master FileOwner · Registered Assessor▾
Assessment Reports
Judgements, learner feedback, remediation agreements, appeals log.
Internal Moderation & Quality FileOwner · Moderator / SDP▾
Moderation Evidence
10% sampling matrix, HACCP/LOTO compliance sheets, SDP sign-off.
Final Accreditation Gateway
Issued by the accredited Skills Development Provider once internal moderation is signed off.
Provider submits declaration + PoE to the Assessment Quality Partner (AQP).
QCTO awards the SAQA-registered certificate on successful EISA outcome.
Audit & Compliance
Evidence & Audit Pipeline
From portfolio assembly to external sign-off — the exact route your evidence travels.
- Step 1
PoE Assembly
Learner evidence, formative records and logbook entries filed against the alignment matrix.
- Step 2
Internal Assessment
Registered assessor judges each KM/PM/WM outcome using the supplied instruments.
- Step 3
Internal Moderation
Sampling and verification of assessor decisions, with remediation loop before submission.
- Step 4
External Moderation
SETA/QCTO desktop audit and certification upload against registered credits.
Broken Standard vs i2Graduates Standard
The measurable delta between improvised material and an audit-ready suite.
Broken Standard
i2Graduates Standard
Curriculum Mapping
Photocopied guides with mismatched outcomes
2 KM + 0 PM + 0 WM modules mapped to NQF Level 7
Assessment Bank
Missing formative and summative assessments
Pre-validated assessment bank per module
Alignment Evidence
No alignment matrix — audit fails
BANKSETA alignment matrix included
Facilitation
Facilitators improvise Chief Information Officer: Cybersecurity delivery
Facilitator scripts + learner activities per credit
Portfolio of Evidence
PoE gaps flagged in moderation
PoE templates that survive external moderation
Pricing & Delivery Tiers
Base licence from R71 000
Digital Master Suite
Editable master files, licensed to your SDP
- Learner Guide, Facilitator Guide & Assessment Suite
- Workplace logbook + alignment matrix (editable)
- Instant digital delivery under institutional licence
- Free minor corrections for 12 months
Turnkey Print & Bound Package
Printed, bound and couriered per learner
- Everything in the Digital Master Suite
- Full-colour print, wire-bound learner packs
- Per-learner PoE folders and dividers
- Nationwide courier with tracked delivery
Full Enterprise Accreditation Bundle
Assets plus accreditation support end-to-end
- Everything in the Print & Bound Package
- Bespoke QMS build mapped to your scope
- Moderation dry-run + written remediation report
- Brand & metadata integration across the suite
Complementary Services
Optional add-ons that harden your accreditation scope before an external audit.
Bespoke QMS Build
We author your Quality Management System — policies, procedures, records, matrices — mapped to your accreditation scope. From R18,500.
Request QuoteModeration Consultation
External moderation dry-run on your PoE + delivery pack. Written report with fixes before your real audit. From R4,900.
Book Moderation SessionThe i2Graduates Quality Guarantee
Every page of this bundle is checked for sequence and structural accuracy — no missing pages, no shortcuts. You get pre-validated assessment instruments ready to survive rigorous compliance moderation, wrapped in a curriculum your facilitators will enjoy teaching.